About
Salih Köse
Cyber Security Advisor
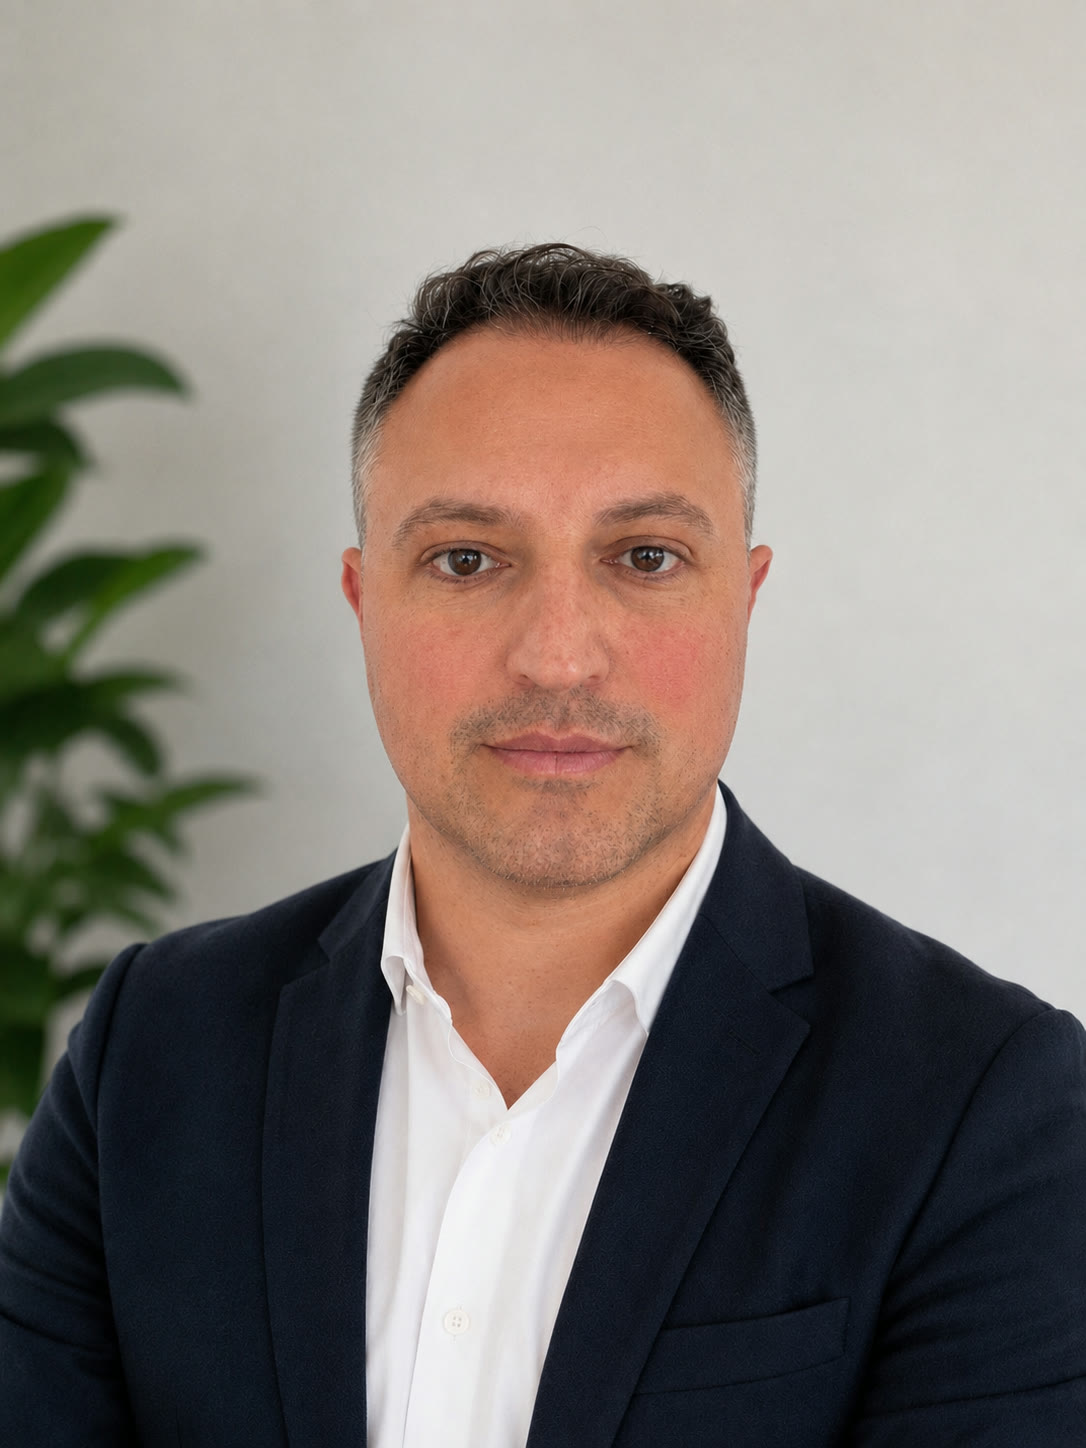
At CyberSteer you work directly with me. My professional background combines hands-on technical cyber security with security operations, information security management, cyber risk and security governance.
Over the course of my career I have held technical, operational and leadership responsibility — from network and security engineering through SOC operations to leading a cyber security function.
- CISM
- Certified Information Security Manager
- CCSK
- Certificate of Cloud Security Knowledge
From technology to security management
Network & Security Engineer
Hands-on work with networks, security technologies and infrastructure — the technical foundations of cyber security.
SOC Lead
Security operations, monitoring, detection, incident handling and the development of SOC processes.
Head of Cyber Security
Cyber security strategy, security governance, cyber risk management and communication with management.
Technical and management perspective
Effective cyber security emerges where both perspectives meet: an understanding of infrastructure, security technologies and operational reality — and an understanding of risk, responsibilities, prioritisation, resources and management decision-making. Recommendations stay technically informed and realistically achievable.
Areas of experience
- Cyber security strategy
- Information security
- ISMS
- ISO 27001
- Cyber risk management
- Security governance
- SOC & security operations
- Security monitoring & detection
- Cloud security
- Network & infrastructure security
- Audit & compliance readiness
- Security management
CyberSteer as a consulting concept
CyberSteer stands for my consulting approach: shaping information security pragmatically, on a risk basis and with an eye on what an organisation actually requires.
Information security should be seen neither purely technically nor purely through a compliance lens. It becomes effective in the interplay of risk, availability, regulatory and contractual requirements, cost, technical options and business goals.
Academic background
- Bachelor's degree in Electrical and Electronics Engineering
- Master's degree related to Information Systems
How I work
- Pragmatic
- Recommendations must be implementable in your actual environment.
- Risk-based
- Prioritisation by risk rather than by checklist.
- Technically informed
- Governance recommendations stay grounded in technical reality.
- Clear
- Risks and options are understandable to both engineers and management.
- Independent
- Recommendations follow your requirements, not a product agenda.
Where does your information security stand today?
An initial conversation helps to clarify the current situation, the priorities and reasonable next steps.