Information Security & ISMS
Establishing, improving and operationalising a management system that fits the size and working reality of the organisation.
Independent cyber security advisory
Information security advisory for organisations that want to understand their risks, build effective security structures and prepare for ISO 27001, NIS2 and customer or compliance audits — without unnecessary complexity.
No obligation · 30 min intro call · No pitch
Advisory areas
Six areas that complement each other in practice. Current core focus: ISO 27001 and building an ISMS that works in day-to-day operations.
Establishing, improving and operationalising a management system that fits the size and working reality of the organisation.
Gap analysis, maturity assessment, documentation structure and support through to the external audit.
Assessing risks in a structured way, interpreting contractual and regulatory requirements and prioritising gaps.
Responsibilities, processes and decision paths that make security manageable over time.
Temporary or ongoing security expertise for organisations without a full-time security function.
Using existing data from operations, monitoring and assessments to focus effort where it matters.
Consulting approach
The focus stays on the risks that actually matter to your organisation.
Measures have to work in real operating environments, not only on paper.
Technical security topics are translated into decisions management can make.
Clear responsibilities, evidence and traceable decisions.
Our approach
From risk assessment through governance and implementation guidance to verification and continuous improvement – a pragmatic approach that aligns security with the risks, requirements and capabilities of your organisation.
Risks & requirements
Governance & ISMS
Security in practice
Assurance & compliance
Security & ISMS
Continuous improvement
The advisor behind CyberSteer
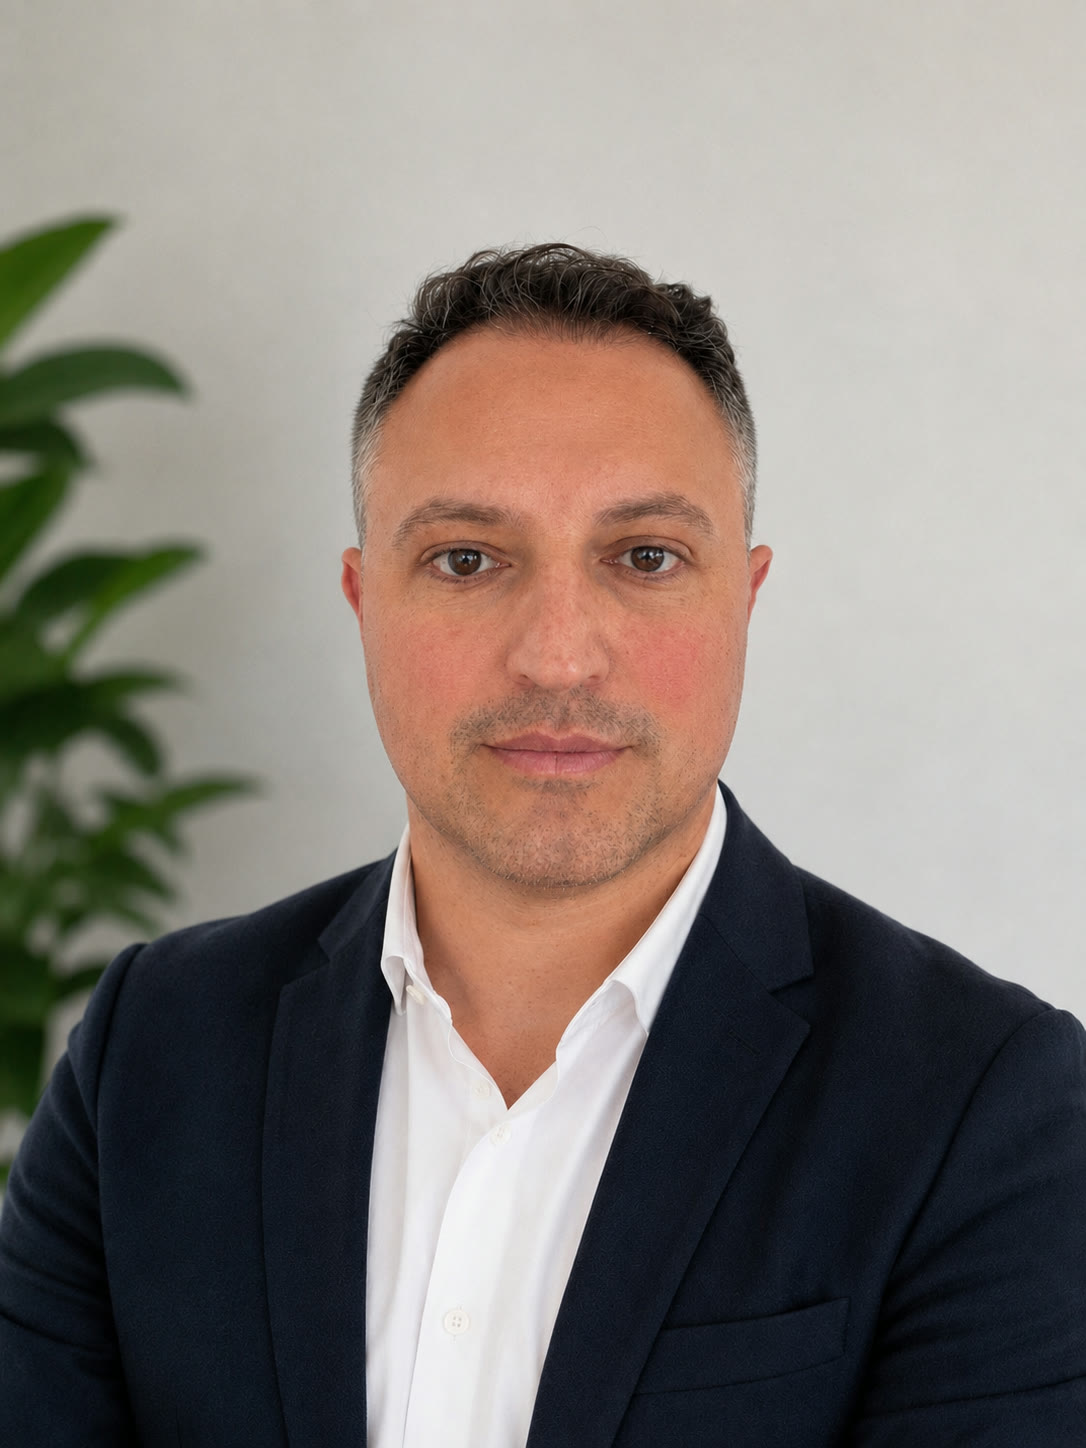
Cyber Security Advisor
You work directly with me, as an independent information security advisor.
My background combines technical cyber security, security operations and security management: from network and security engineering through leading a SOC to responsibility for cyber security at organisational level, including international and regulated environments.
Insights
Articles on ISO 27001, ISMS, cyber risk, security governance and security operations.
Information Security
Information security should reflect an organisation’s actual risks, requirements and capabilities. The key is setting the right priorities and building a realistic path forward.
Salih KöseReading time: 7 min
An initial conversation helps to clarify the current situation, the priorities and reasonable next steps.